Inside the platform
What it looks like running
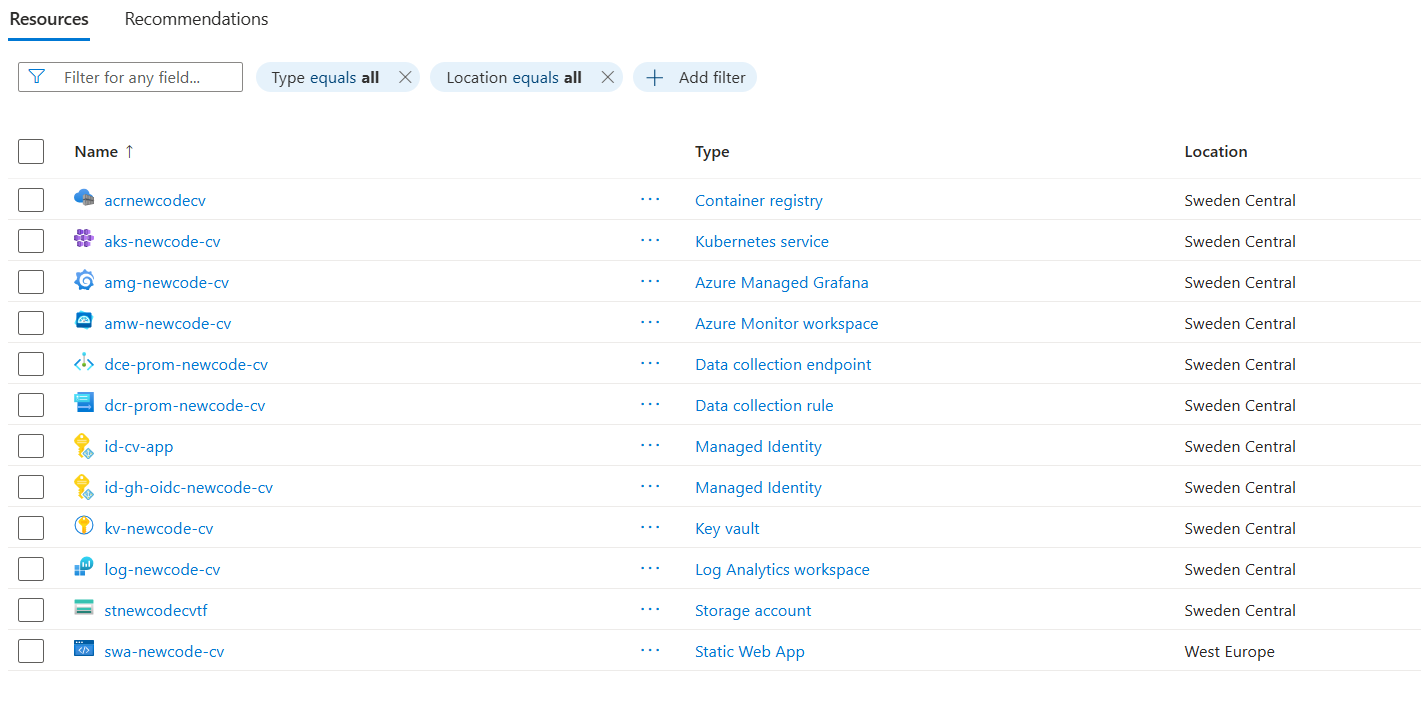
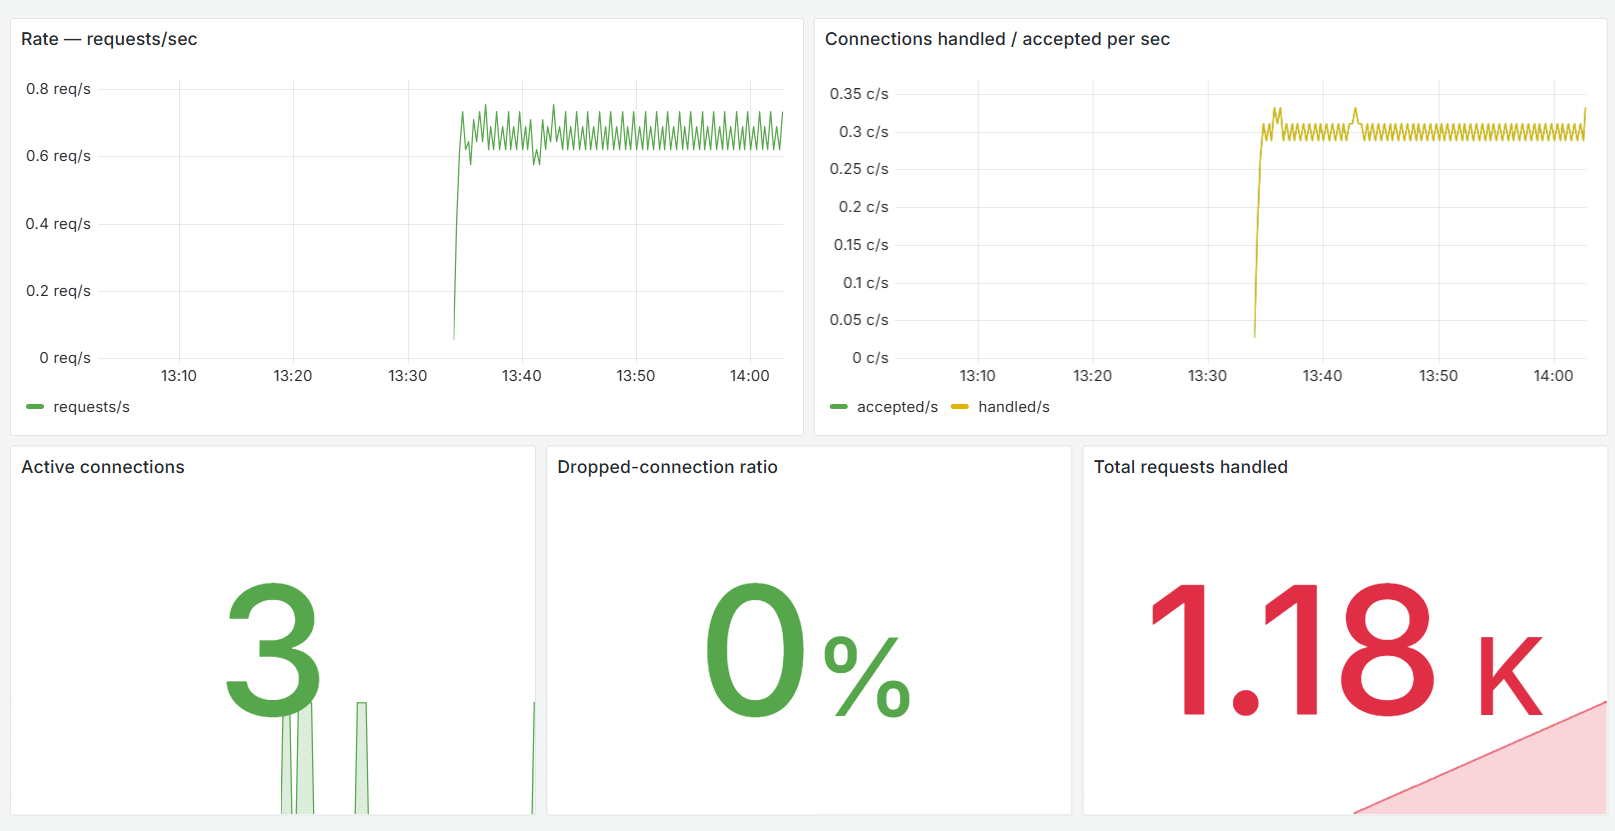
The cluster's own Grafana and the Azure resources behind it. Screenshots are local assets - no remote images, so the page still makes zero external requests.
Michał Sulawiak
I build and run production Azure and AKS platforms. The site you're reading is deployed by the same pipelines it documents - the code is all in this repo.
Cluster offline
The full private-AKS platform - the app, the signed image, real metrics - now runs on request instead of on a schedule: I start a window by hand and tear it down afterwards, so it costs nothing when idle. Want to see it running? Get in touch and I'll bring the cluster up for you.
Static Web Apps + AKS
Right now you're on the always-on front, served by Azure Static Web Apps. The same build runs on a private AKS cluster, deployed by Helm, during an on-demand live window.
kubectl
output - to
docs/evidence.
Captured by the deploy-aks pipeline and committed to the repo - view the full run ↗.
Inside the platform
The cluster's own Grafana and the Azure resources behind it. Screenshots are local assets - no remote images, so the page still makes zero external requests.
Newcode.ai role
Each row links to the file in this repo that backs it.
| # | Requirement | What's there | Proof in this repo | ✓ |
|---|---|---|---|---|
| 01 | Azure (IaC) | Whole platform - RG, AKS, ACR, Key Vault, monitoring - is Terraform. | terraform/aks.tf | ✓ |
| 02 | AKS | Private-API-server cluster; nodes, identities, add-ons codified. | terraform/aks.tf | ✓ |
| 03 | Terraform | azurerm remote state; pinned providers; OIDC plan/apply in CI. | terraform/main.tf | ✓ |
| 04 | Helm | cv-site chart: Deployment, HPA, PDB, ServiceMonitor, NetworkPolicy. | helm/cv-site/Chart.yaml | ✓ |
| 05 | GitHub Actions | Build, scan, sign, then helm-upgrade to private AKS over Tailscale. | .github/workflows/deploy-aks.yml | ✓ |
| 06 | Multi-tenant isolation | Per-tenant namespaces with default-deny NetworkPolicy. | helm/cv-site/templates/networkpolicy.yaml | ✓ |
| 07 | Model-serving infra | Reproducible container + Helm pattern for serving any AI workload. | docs/architecture.md | ✓ |
| 08 | Monitoring / alerting | Managed Prometheus ServiceMonitor + Grafana RED dashboard + SLO. | SLO.md | ✓ |
| 09 | Security | Zero secrets in repo: OIDC, Key Vault + CSI, gitleaks, Trivy, cosign. | SECURITY.md | ✓ |
| 10 | AI agents | How this platform hosts agentic AI workloads for legal/pro services. | docs/ai-agents.md | ✓ |
15+ years in production infrastructure
A dozen-plus smaller companies
Alongside contracting, I've delivered automation and platform work for a dozen-plus smaller companies - software houses, businesses automating their operations, IT product teams, and my own back office. A few of them:
OIDC · Key Vault · cosign
Azure auth uses GitHub workload-identity federation. No service-principal secrets exist in the repo or CI.
In-cluster secrets (like the tunnel token) come from Azure Key Vault through the Secrets Store CSI Driver and Workload Identity.
gitleaks runs pre-commit and in CI; a detectable secret fails the build before it merges.
Trivy blocks HIGH/CRITICAL CVEs; cosign keyless signs every image and the deploy verifies that signature.
Engagement
This whole platform - AKS, signing, monitoring, tenant isolation - is built and run by the pipelines in this repo, starting from an empty Azure subscription. If that's what you're hiring for, get in touch.